TryHackMe - Sakura
Published:
Use a variety of OSINT techniques to solve the room created by the OSINT Dojo.
Task 2
- I downloaded the image left by the attacker at picture link.
- Then I used exiftool to extract the picture informations:

- From the export-filename, I figured out that the attacker’s username is: SakuraSnowAngelAiko
Task 3
- Many people become attached to their usernames, and may therefore use it across a number of platforms, making it easy to find other accounts owned by the same person when the username is unique enough.
- I searched the attacker’s username on google and was able to find a github account and a twitter account with the same username.
A post on their Twitter account reveals their main account which is AiKOABE3. So their name must be Aiko Abe.
- It was challenging to find the attacker’s email. I found zero information about it on Twitter, then started searching through their Github account and found a PGP key repo.
- When creating a PGP key, users may enter information such as a name, username, or email address which later can be extracted from their public key. So I copied their public key and import into Kleopatra to extract the informations from the key.
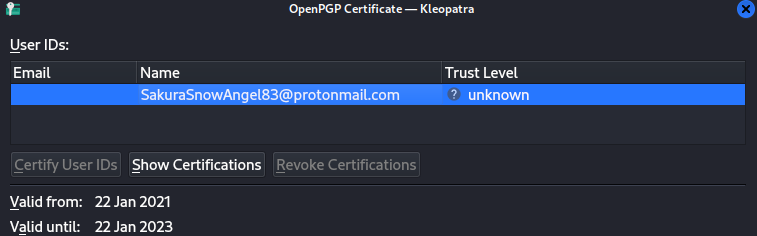
- So their email is: SakuraSnowAngel83@protonmail.com
Task 4
- There are multiple repos on their github account, one of them named ETH, so I guess it must be related to their crypto wallet. Looking at the current version of the miningscript, there is nothing much. But looking at the history version of the file, I found their wallet address:
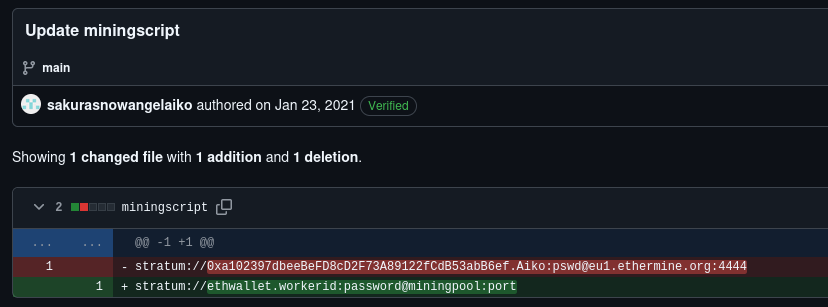
- Using their wallet address: 0xa102397dbeeBeFD8cD2F73A89122fCdB53abB6ef on Blockchain, I can track their history transactions. The mining pool the attacker received payments from on January 23, 2021 UTCT was: Ethermine

- The other cryptocurrency the attacker exchanged is: Tether

Task 5
- The attacker’s current Twitter handle was already found at task 2: SakuraLoverAiko
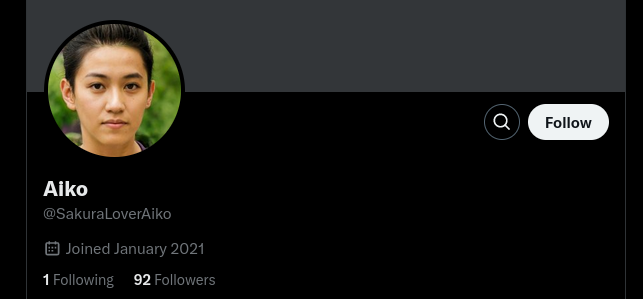
- From the attacker’s posts on Twitter, it looks like they store they Regular wifi and passwords somewhere on the Dark Web.
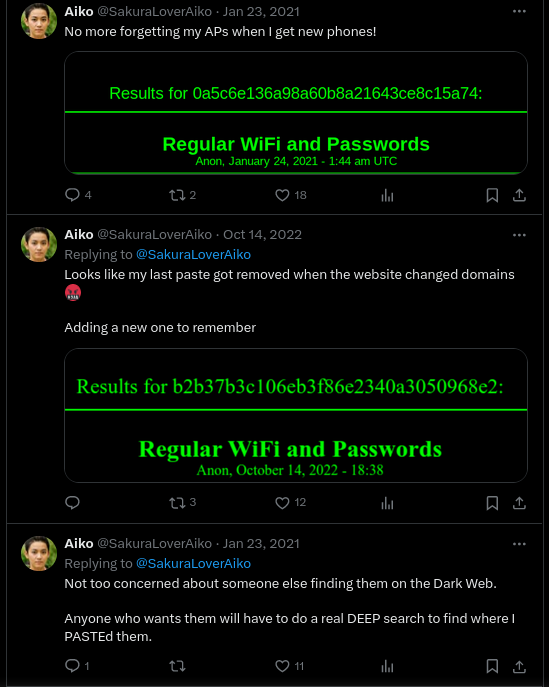
- Their post on 23th Jan, 2021 emphasized that: “Anyone who wants them will have to do a real DEEP search to find where I PASTEd them”. So the website must be something related to DEEP PASTE, isn’t it?
- I actually found a website https://deepweblinks.net/pastebin/ using Tor, but the links provided by the website no longer work. So the last solution is to use the hint image provided.
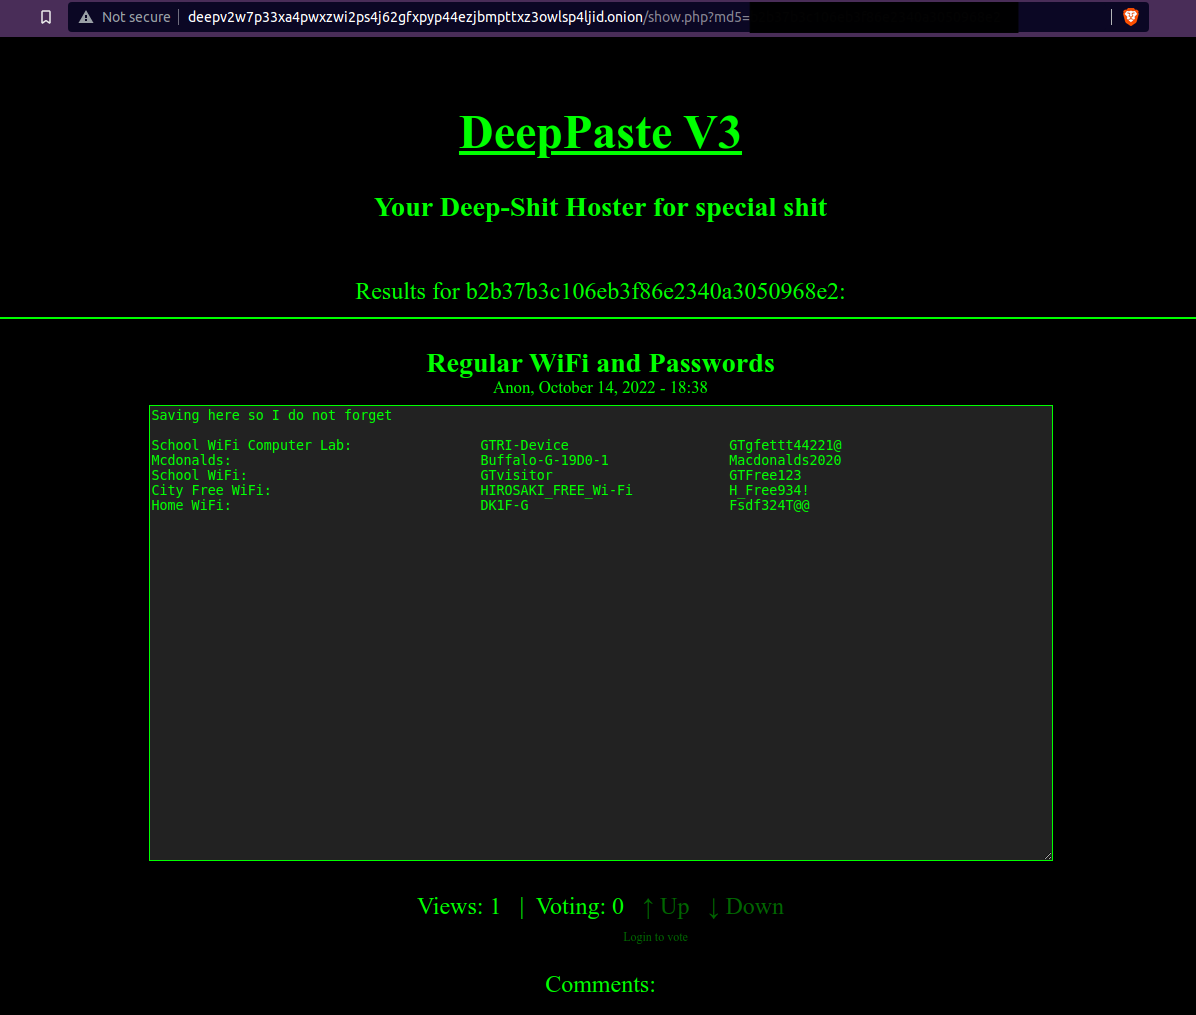
The URL for the location where the attacker saved their WiFi SSIDs and passwords is: http://deepv2w7p33xa4pwxzwi2ps4j62gfxpyp44ezjbmpttxz3owlsp4ljid.onion
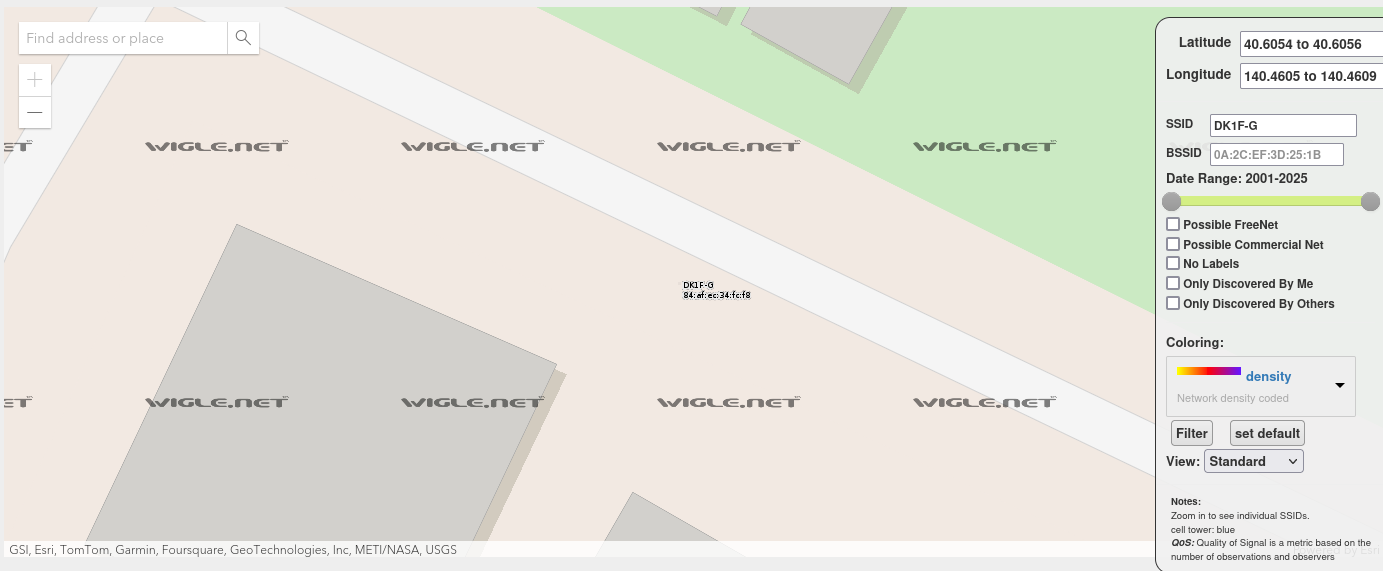
Based on their home wifi information on DEEP PASTE: “DK1F-G Fsdf324T@@”. I performed a search on Wigle with SSID being DK1F-G and was able to find their location which is close to Hirosaki as well as BSSID: 84:af:ec:34:fc:f8
Task 6
- This is the last image they posted before they head home:
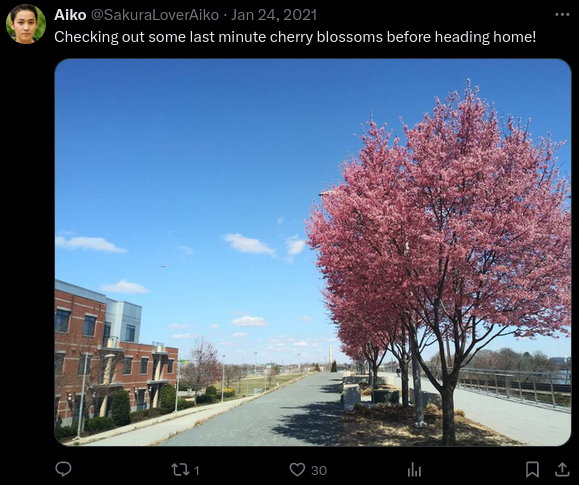
- At first, I was sure this is Japan because: 1/All of their informations lead to Japan and 2/I see a cherry blossom. I took a lot of time searching thourgh Japan airports but there was no result.
- It was not until when I changed the searching object to the below picture, the result return that it is actually the Washington Monument:
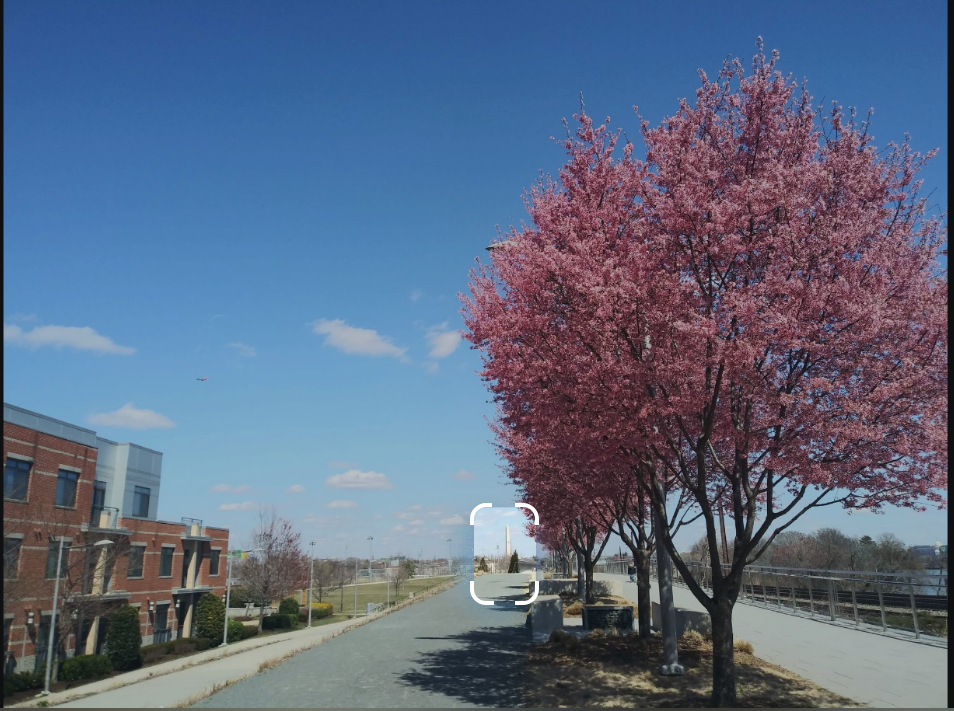
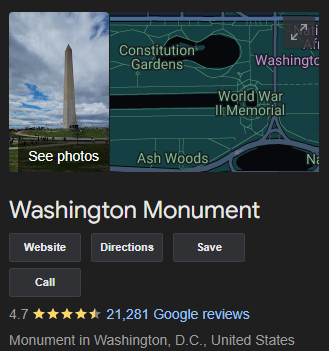
So I did a search for airports near the area and found Ronald Reagan Washington National Airport or DCA
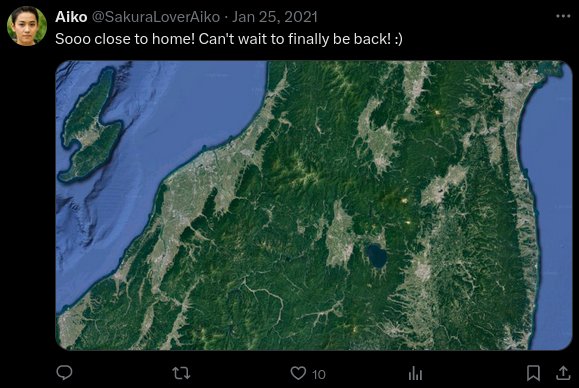
The rest questions are much more easier. Here are the other two posts I used to find the answer to other questions:
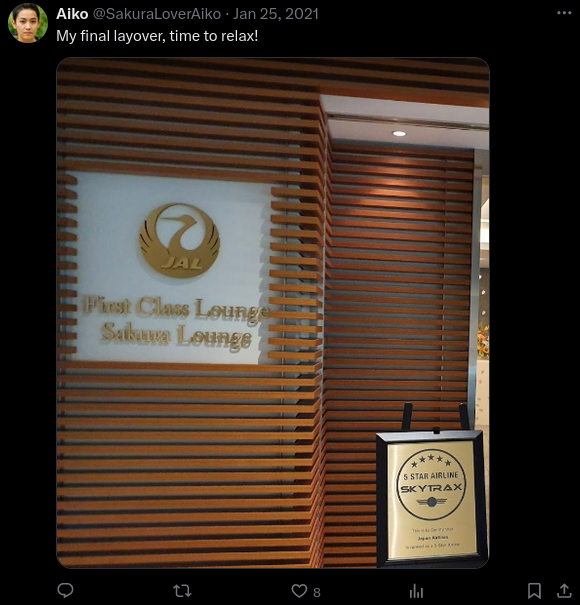
- To find the last airport the attacker had their last layover in, I use Google with keyword: “JAL First Class Lounge Sakura Lounge” and there’s only one airport that has the same lounge as in the picture which is Haneda airport - HND.
- The name of the lake is Lake Inawashiro:
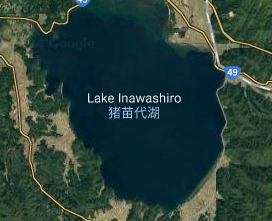
- The attacker’s hometown is Hirosaki because we know the location of their home wifi.