Internal Penetration Testing Lab
Overview
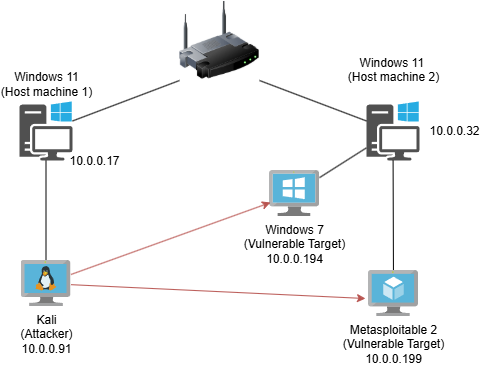
This project involves the creation of a virtualized penetration testing environment for hands-on cybersecurity research and offensive security training. The lab consists of three core virtual machines hosted on two systems:
Kali Linux (attacker system)
Metasploitable 2 (vulnerable Linux target)
Windows 7 (legacy Windows target)
Tools
Nmap – for network and service discovery
Nmap Scripting Engine (NSE) – to run targeted vulnerability checks
Nessus – for in-depth vulnerability scanning and reporting
Metasploit Framework – for exploiting identified vulnerabilities and post-exploitation
Key Takeaways
Developed hands-on proficiency in the penetration testing kill chain: reconnaissance → scanning → exploitation
Practiced using industry-standard tools to simulate real-world attack scenarios in a safe environment
Gained insight into system misconfigurations and exploitable weaknesses in outdated OS platforms